Certifications and regulatory compliance
Accevo MES/MOM is engineered for regulated manufacturing: pharma, FMCG, tobacco, automotive and more. Data integrity and traceability decide whether your product ships or your line stops.
3 x ISO certified
ISO 9001 quality, ISO/IEC 27001 security and ISO 22301 business continuity, independently audited.
Pharma-grade compliance
21 CFR Part 11, EU GMP Annex 11, ALCOA+ and GAMP 5, the sttrictest regime we build to.
CRA & NIS2 ready
Security by design, a working vulnerability process and supplier evidence, ahead of the EU dealdines.
6 regulated industries
Pharma, FMCG & food, tobacco, packaging, automotive and aviation, on a single compliance core.
The next audit won't wait for your legacy MES
Regulatory requirements for manufacturing software are tightening on a fixed schedule. Systems designed a decade ago, or built as in-house custom code, were rarely built with today’s EU requirements in mind.
NIS2
Manufacturers across pharma, FMCG, automotive and aviation are classified as essential or important entities. They must prove cybersecurity across their software supply chain, including the MES.
CRA reporting obligations
Manufacturers of software with digital elements must report actively exploited vulnerabilities and severe incidents. Your MES vendor has to run that process today.
CRA full application
Secure-by-design, SBOM transparency and defined support periods become market-access requirements in the EU. Legacy platforms without a compliance roadmap face end-of-life.
Modern compliance, without the multi-year migration
Fast implementation
Compliant with current requirements
Configuration that replaces custom code
Bring your history with you
Everything an auditor will ask about
Certificaciones de la empresa
ISO 9001 – un sistema de gestión de la calidad certificado que abarca el desarrollo, la entrega y el soporte técnico.
ISO/IEC 27001 – Gestión de la seguridad de la información certificada; tus datos de producción están protegidos por controles de seguridad auditados de forma independiente.
Comprueba quiénes somos – Copias de certificados, declaraciones de alcance y pruebas de auditoría relativas a la cualificación de sus proveedores, disponibles en cualquier fase de la evaluación.
Pharma regulatory compliance
21 CFR, Parte 11, de la FDA y el Anexo 11 de las BPF de la UE – secure audit trails, unique user authentication, role-based access and electronic signatures with meaning and manifestation.
ALCOA+ por diseño – cada registro debe ser atribuible, legible, contemporáneo, original y preciso, con un historial completo de cambios que conserve todos los valores anteriores.
Registros electrónicos de lotes – Revisión por excepción, flujos de trabajo obligatorios y genealogía completa de los lotes para agilizar el lanzamiento, con pleno cumplimiento de las buenas prácticas de fabricación (GMP).
Validation support
Ajustamiento a GAMP 5 (2.ª edición) – Desarrollado e implementado como un producto configurable, lo que permite un enfoque de validación simplificado y basado en el riesgo.
Compatibilidad con CSV/CSA – Paquetes de documentación de validación estándar, trazabilidad de los requisitos y apoyo en la ejecución de IQ/OQ/PQ.
One compliance core for every regulated industry
Pharmaceutical & Life Sciences
FMCG & Food
Tabaco
Serialization and track & trace aligned with EU Tobacco Products Directive requirements, with unit-to-pallet aggregation and reporting integration on the production line.
Automoción
Full product genealogy, enforced process interlocking and complete quality records, the evidence base your IATF 16949 system and OEM audits demand.
Aviación
Part-level genealogy, operator certification control and airworthiness-grade records retention, supporting AS/EN 9100 quality systems and authority audits.
Embalaje
Material and lot traceability across converting and filling lines, customer-specification enforcement and audit-ready quality documentation.
Security built in before the first login
Security is embedded from architecture through release. Our ISO 27001-certified development lifecycle includes threat modeling, secure coding, dependency and vulnerability scanning, code review and controlled releases.
The platform ships hardened by default: role-based access with least privilege, TLS-encrypted communication, corporate identity integration (LDAP/AD, SSO), configurable password and session policies, full audit logging, and an architecture ready for IEC 62443 zone-and-conduit network segmentation.
EU Cyber Resilience Act readiness
NIS2 for your supply chain
Patch & vulnerability management
Built on the standards your engineers already use
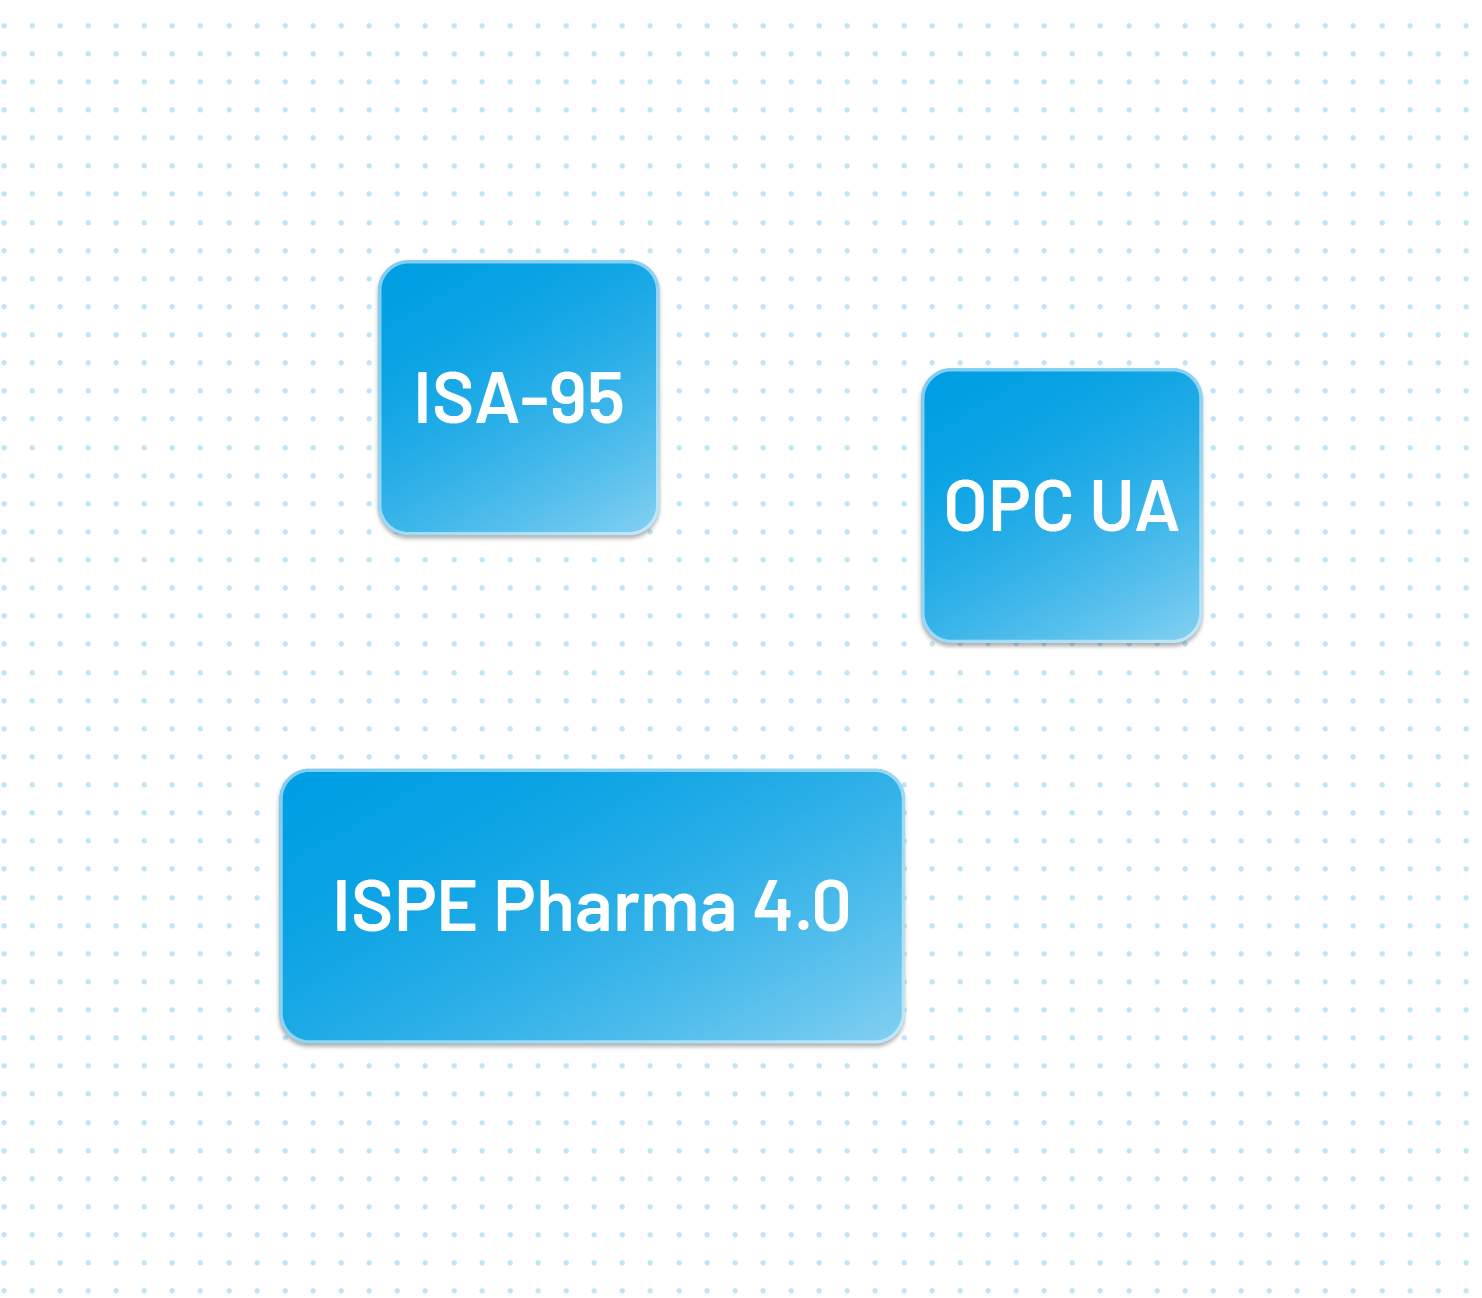
Accevo integrates enterprise to shop floor through ISA-95 and connects machines through OPC UA for secure, vendor-neutral connectivity. Our approach to digital maturity in pharmaceutical manufacturing follows the ISPE Pharma 4.0 operating model, connecting data integrity, digital plant maturity and workforce enablement into a single roadmap for regulated production.
Find out where your current MES fails the 2027 test
Request a compliance gap assessment. We map your legacy system against Part 11, Annex 11, CRA and NIS2 requirements and show you a realistic migration path.
MES compliance questions we hear in every audit and RFI
Accevo MES/MOM provides the technical controls required for compliant electronic records and electronic signatures under FDA 21 CFR Part 11 and EU GMP Annex 11: secure, time-stamped audit trails, unique user authentication, role-based access control, electronic signature workflows and record protection throughout retention periods. Final compliance is achieved in your validated environment, which we support with standard validation documentation.
Accevo Sp. z o.o. holds three independently audited management system certifications: ISO 9001 (quality management), ISO/IEC 27001 (information security management) and ISO 22301 (business continuity management).
Yes. Accevo is aligning its product lifecycle with the CRA ahead of its application dates: secure-by-design development, a defined vulnerability handling process ([email protected]), security updates across the support period and SBOM availability. For customers regulated under NIS2, we provide audited supplier evidence, including ISO 27001 and ISO 22301 certification, incident response cooperation and supplier due diligence support.